KUALA LUMPUR – An online threat intelligence company has raised concerns over a potential cyberattack involving the Melaka Islamic Religious Council’s (MAIM) website, suggesting that the breach may be part of a ransomware operation.
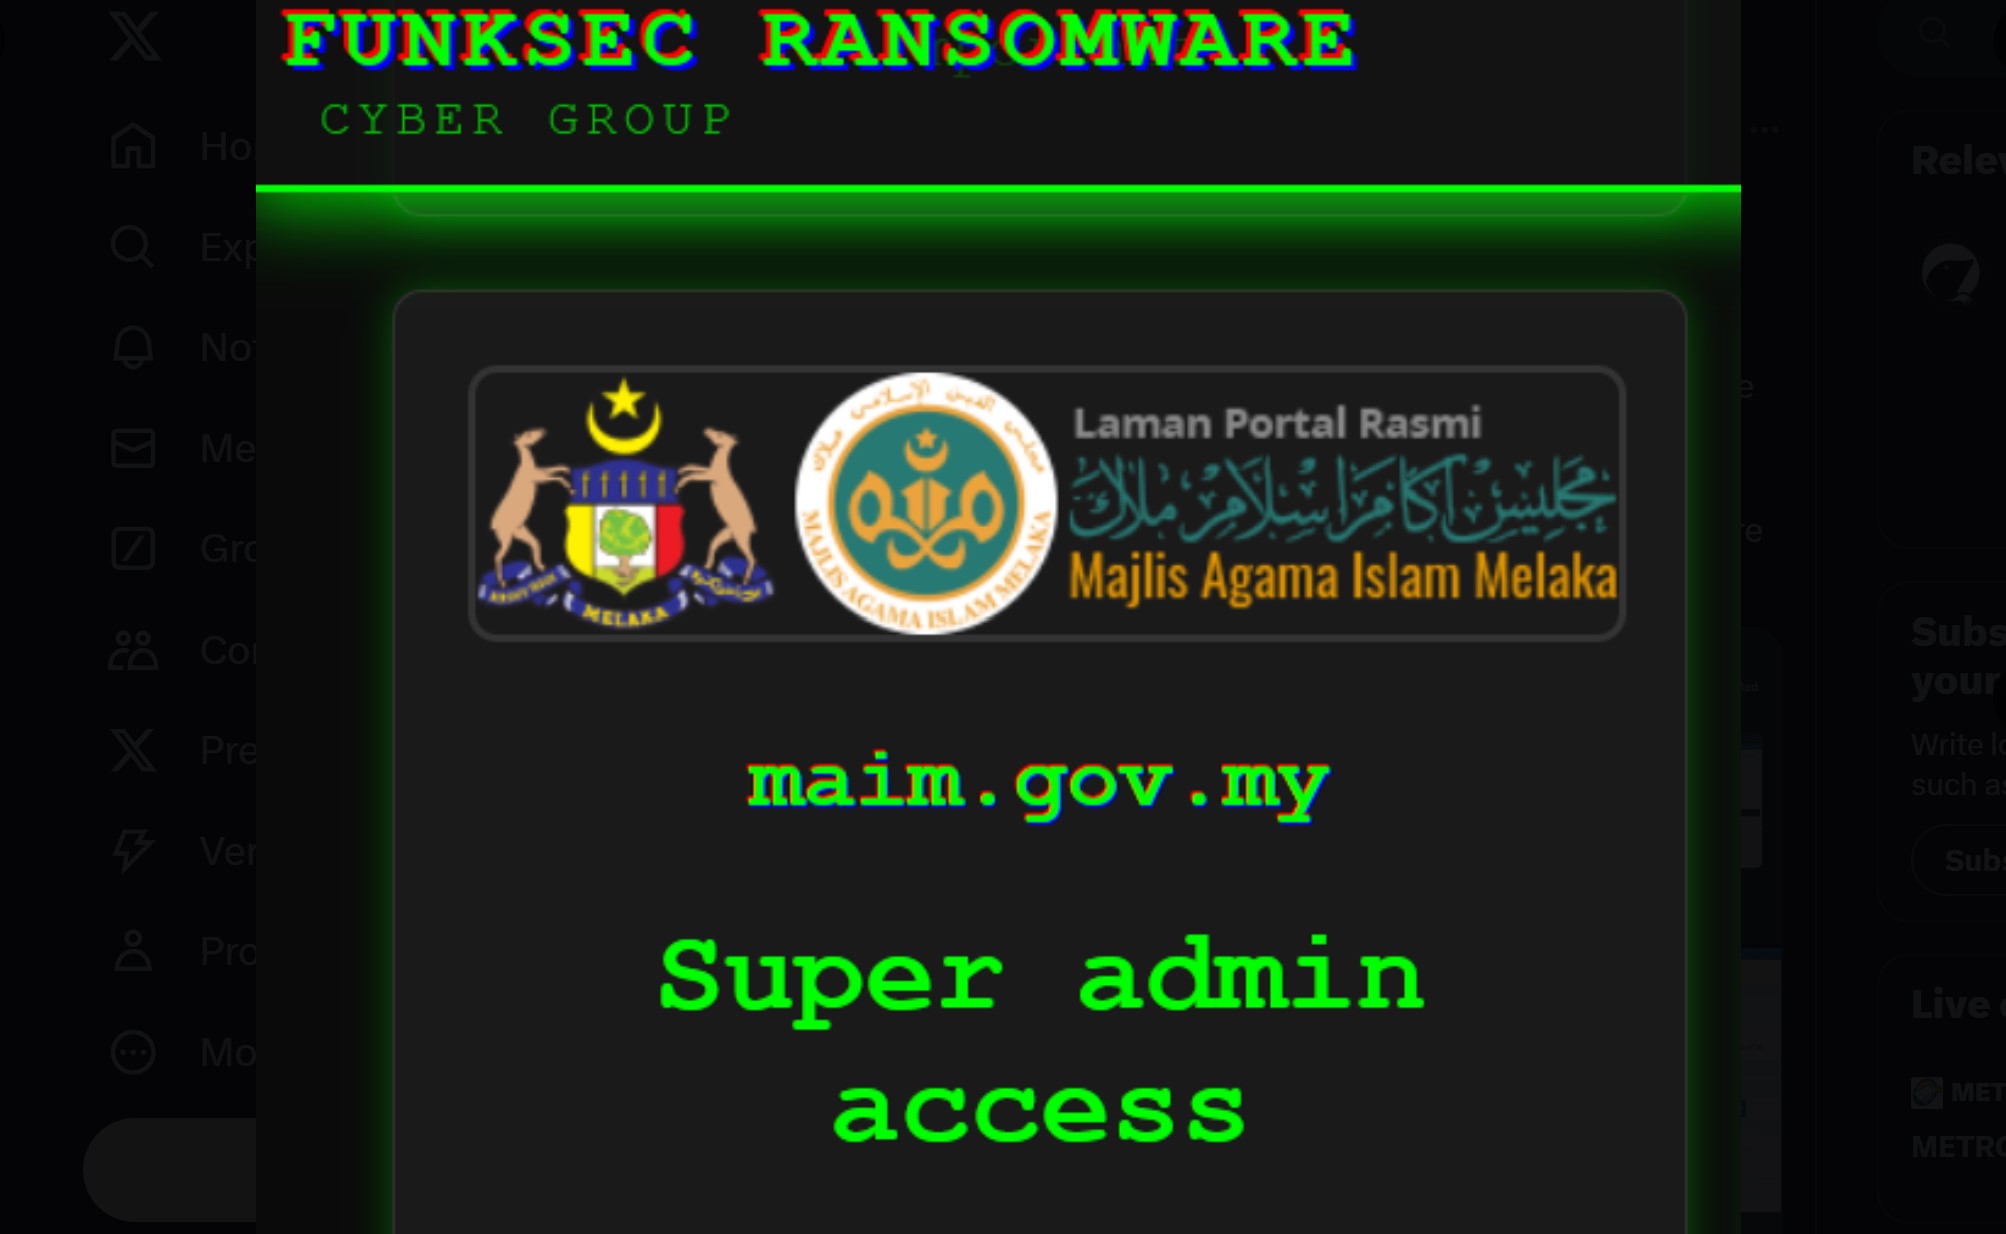
In a post on X, StealthMode, a deep and dark web threat intelligence company, claimed that the Funksec ransomware gang had advertised access to the super admin account of MAIM’s website on its dark web platform.
“They (Funksec) shared a screenshot as proof of logging in as a super admin and claimed they are selling the access for (US)$1,000,” the firm, which aims to identify and eliminate digital risk and criminal activity, said in the post.
In a separate post just minutes later, StealthMode shared that the same ransomware gang has also put up for sale – at the same price – access to the super admin for the Vietnamese Health Ministry’s official website.
A website super admin refers to a user account with the highest level of access to a website or network, with the ability to perform almost any action on the site, including managing features such as privacy settings.
Australian news site Cyber Daily reported on December 12, 2024 that Funksec is a relatively new operation, having posted its first victim on its leak site earlier that month while the site itself is understood to have been created in September last year.
The cybersecurity daily also said that Funksec runs a “for-profit, ransomware-as-a-service operation”, with some of its leak activity said to be “highly politically motivated” as it noted in its targeting manifesto that it has earmarked the United States.
“Our ransomware attacks and operations will target the USA. As a country whose rule depends on first-class support for Israel, the United States weakens the Middle East due to its energy resources, including oil,” Funksec said in its targeting manifesto, as quoted by Cyber Daily.
Previously, Scoop reported that over 300GB worth of Prasarana Holdings Bhd’s private company files were made available in the public domain following a ransomware attack against the public transportation provider.
The data publishing came after cybercriminal gang RansomHub, which claimed responsibility for the attack, had on August 25, 2024 given Prasarana one week to pay an unknown ransom amount.
On August 26, Prasarana confirmed that it was the victim of a ransomware attack in a statement to the press.
Prasarana said that the attack involved unauthorised access to the company’s internal system, adding that their cybersecurity team is handling the situation. – January 1, 2025